Information Security Incident & Breach Response Kit (Excel + Word) — the register, the POPIA s22 decision, the Regulator pack, the notices and two tabletop exercises
An incident process that answers the questions in order on the day — is it an incident, how bad, is it a breach, who must be told and by when, what do we write, what do we keep — and that has been exercised before it is needed.
When something happens the questions arrive faster than the facts: is it an incident, how bad, is it a POPIA breach, who must be told and by when, what do we write, what do we keep. This kit answers them in order.
Instant download through Payhip · no delivery charge · 14-day full refund
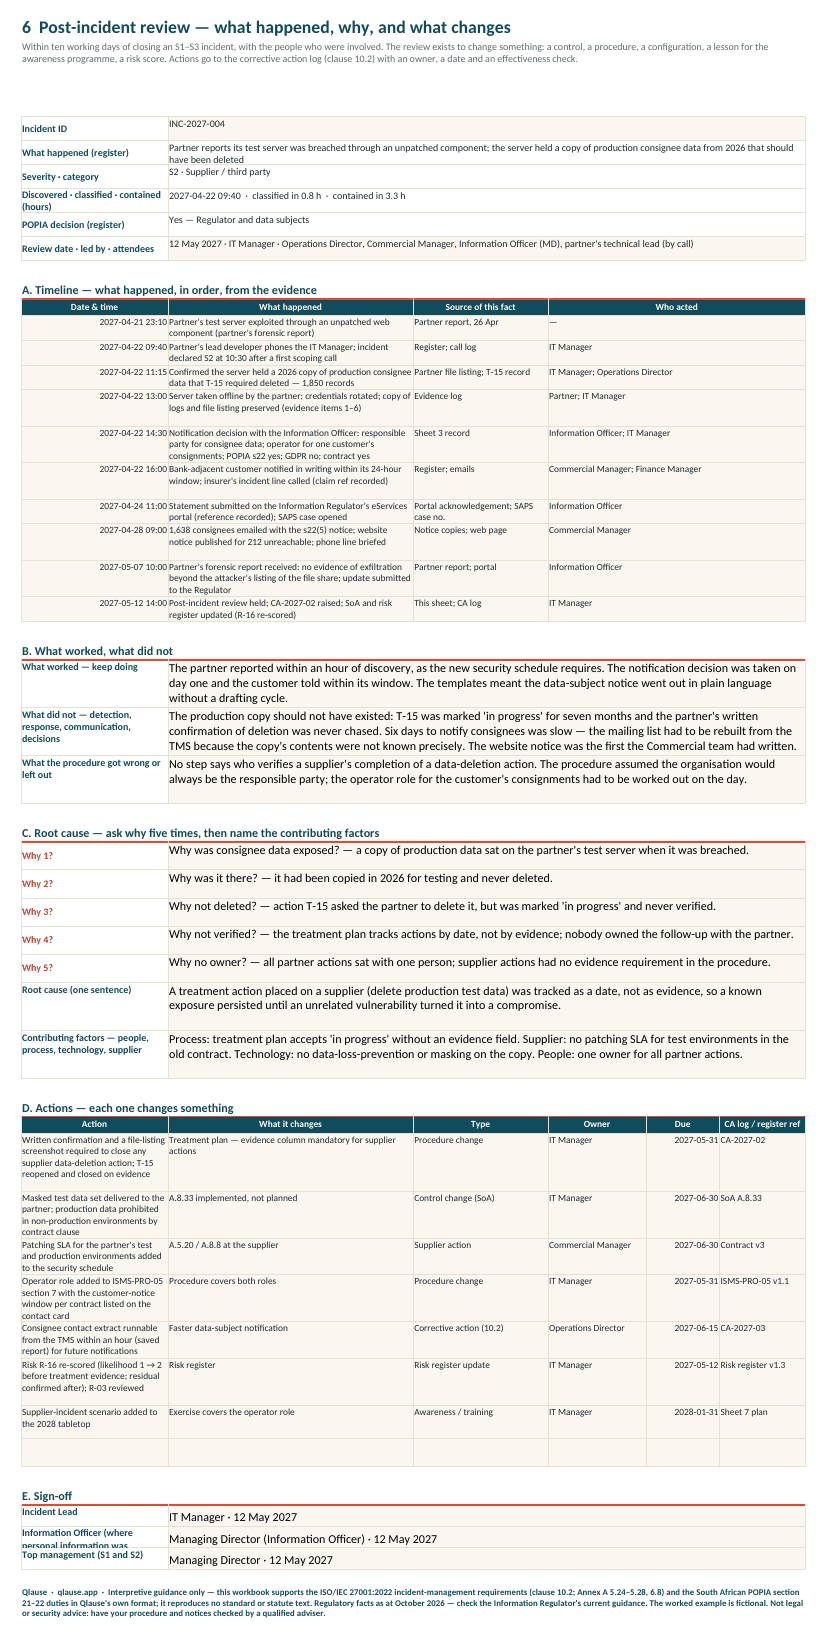
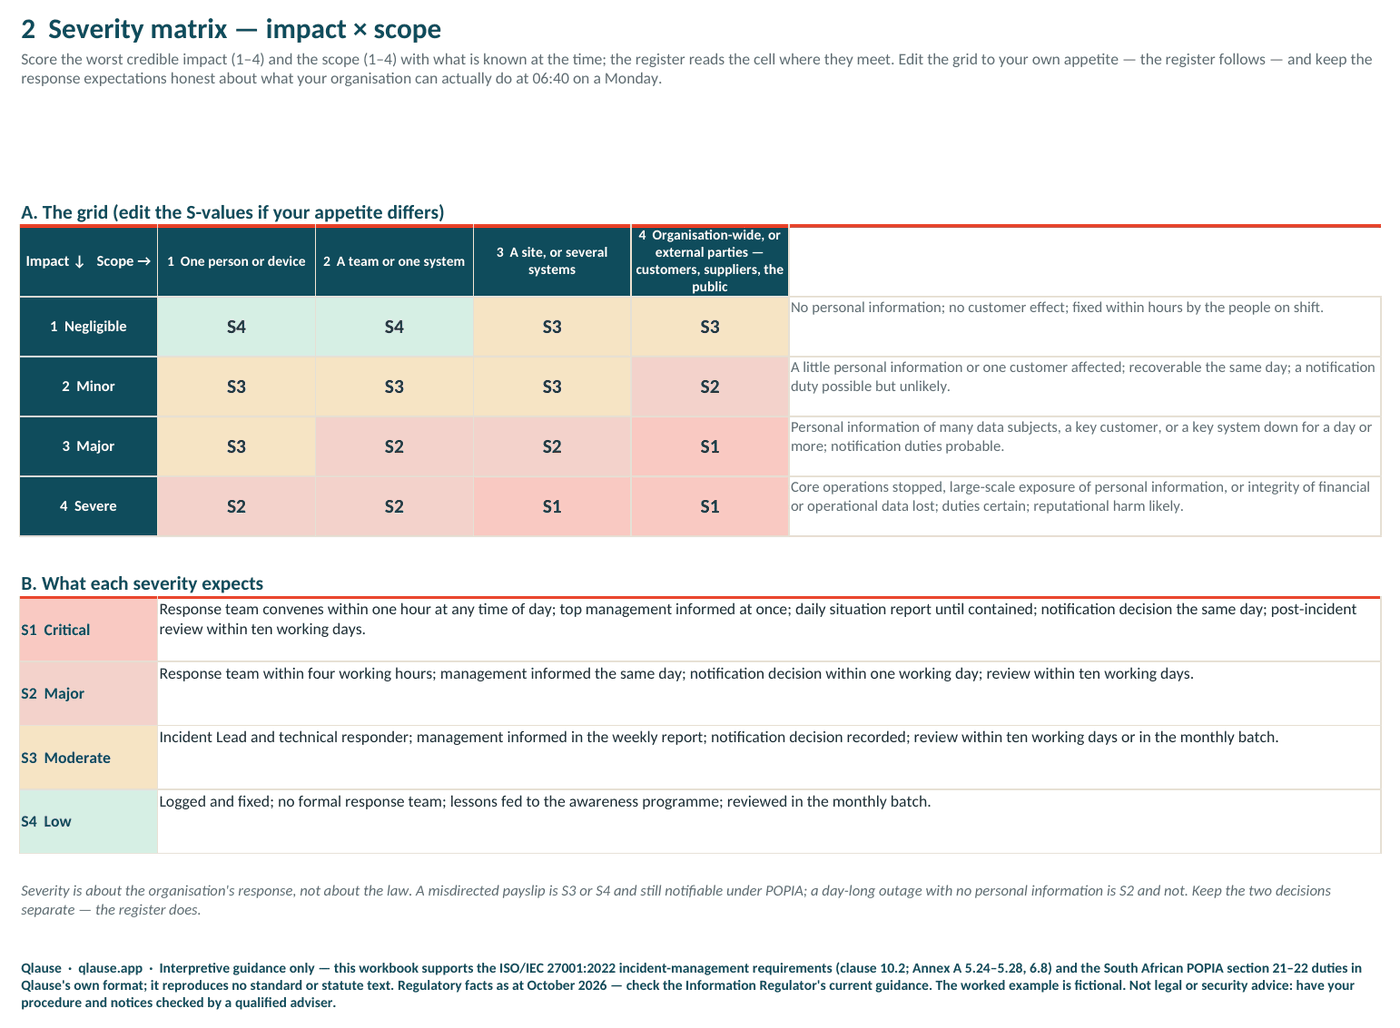
Real pages from the actual files — click any preview to enlarge.
What's inside
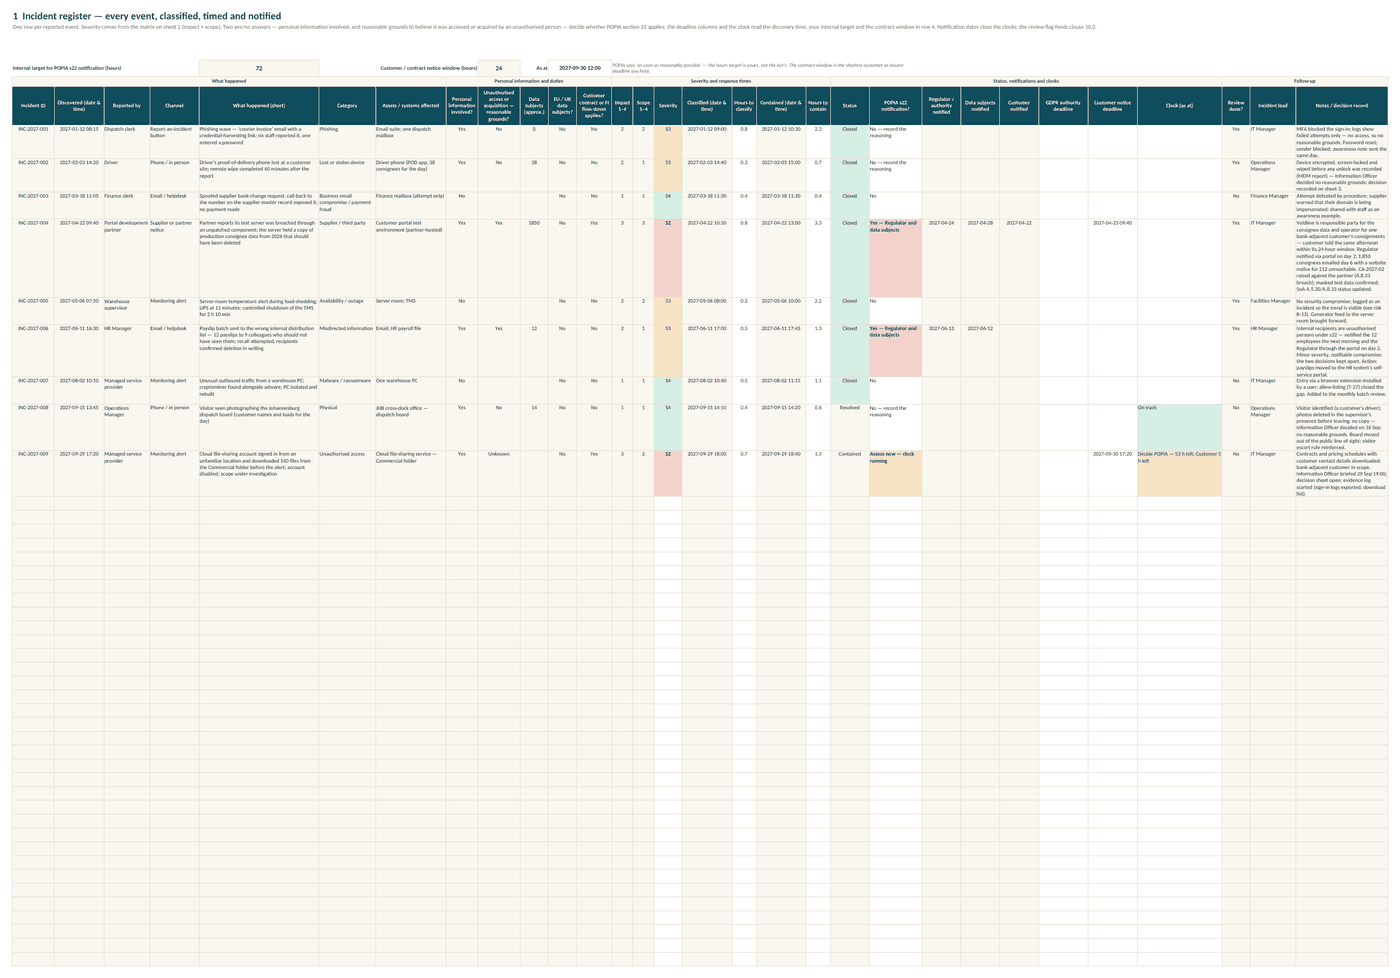
Incident register
Classification, severity from the matrix, hours to classify and contain, the POPIA s22 answer from two yes/no fields, GDPR and customer-notice deadlines, a live clock, notification dates and the review flag.
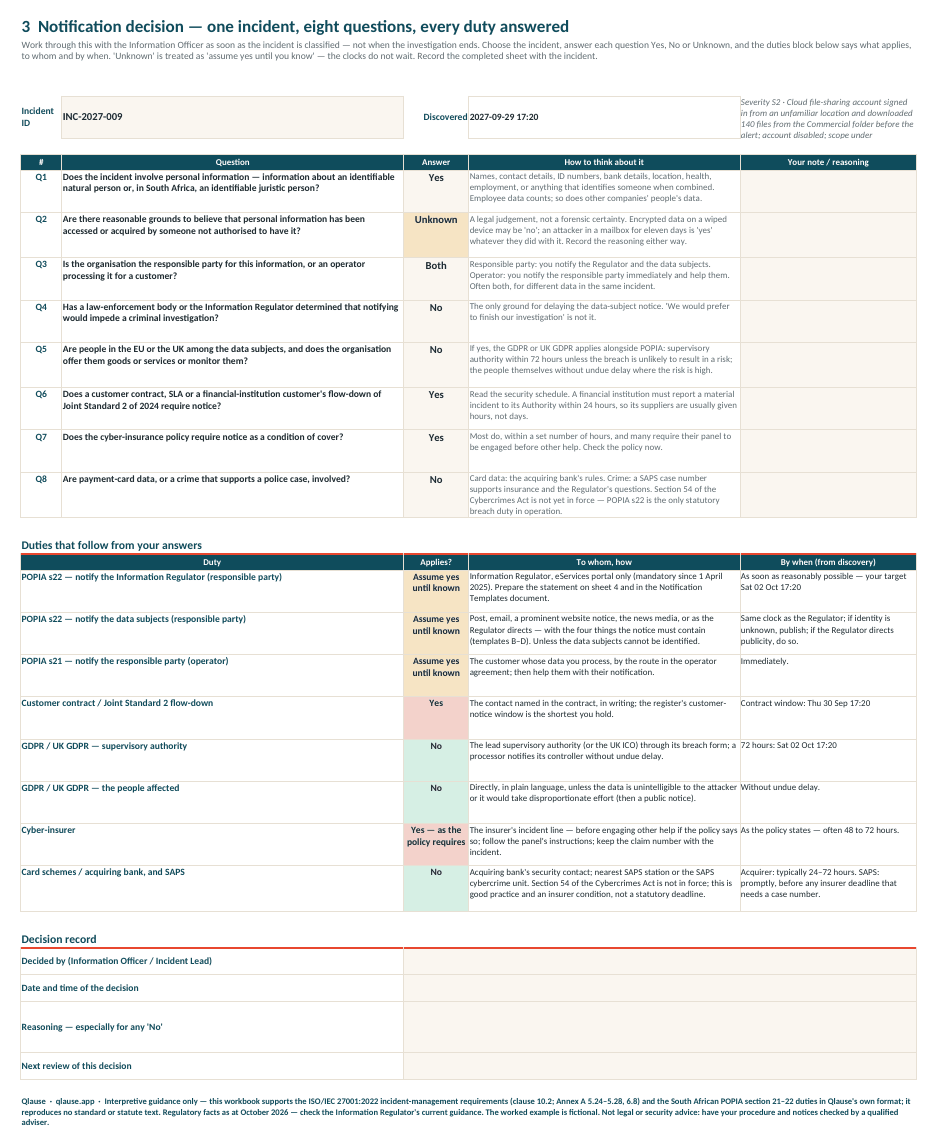
Notification decision
Eight questions for one incident; which duties apply, to whom and by when, with deadlines calculated from the discovery time.
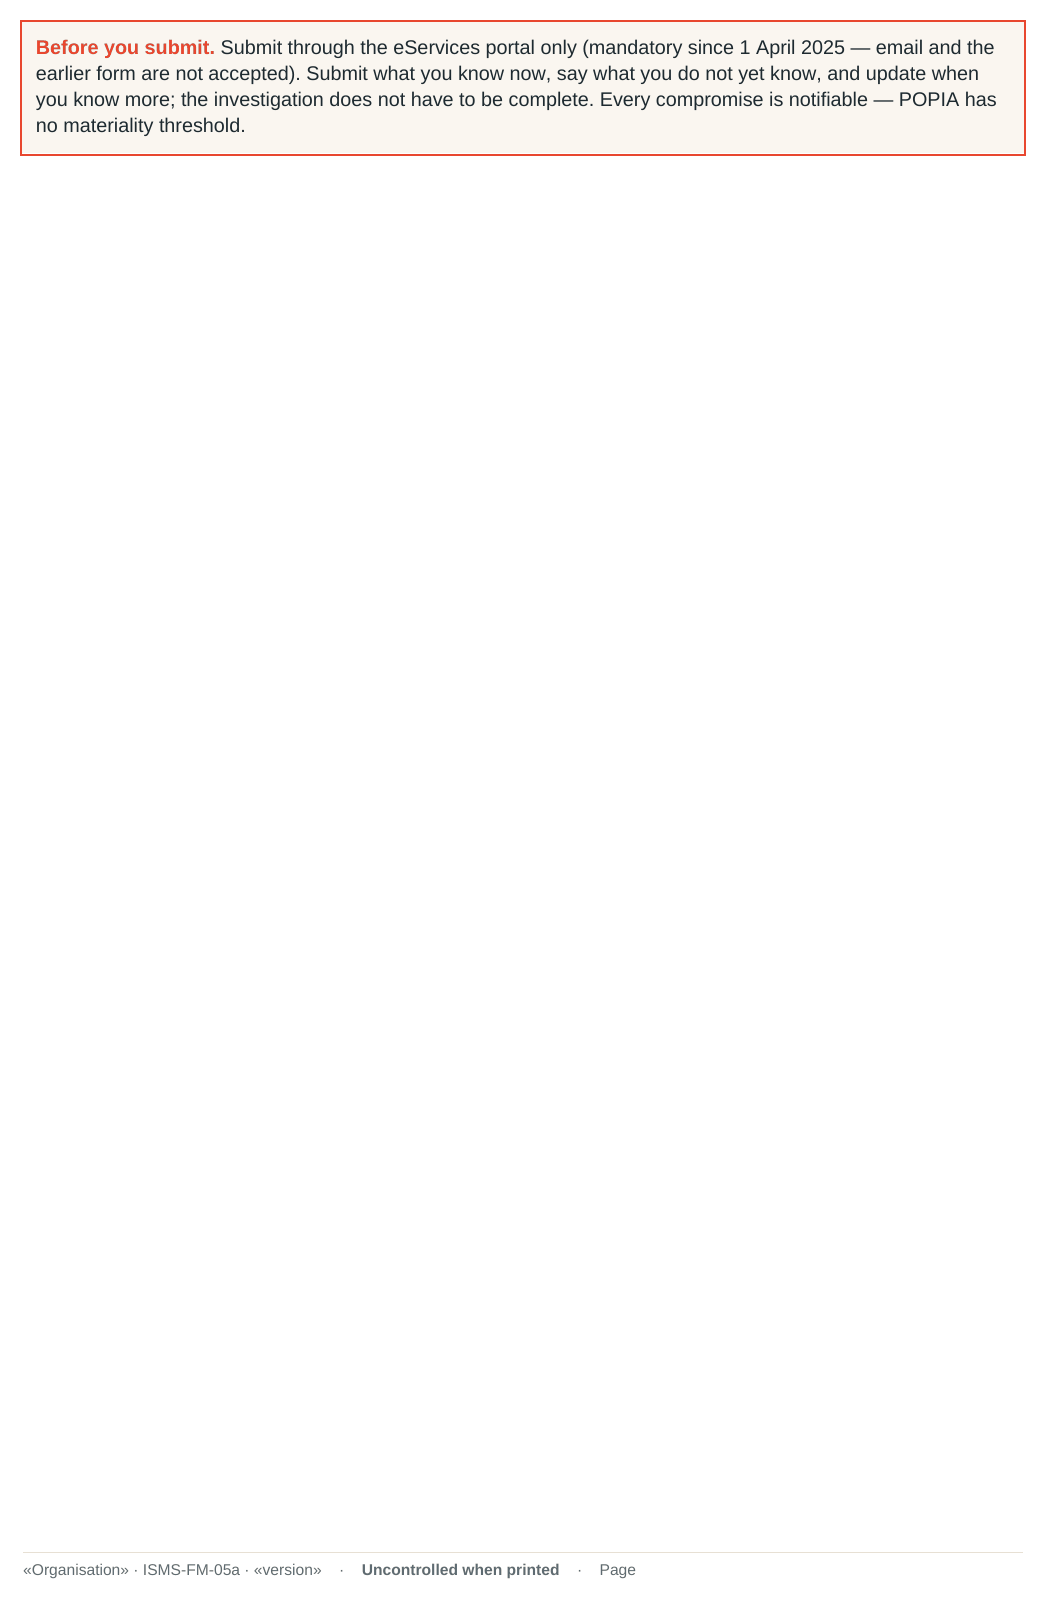
Regulator checklist and notification templates
The thirteen-item pack for the eServices portal, the s22(4) method choice and the timeline; the Word templates for the portal statement and for email, letter and website notices to data subjects.
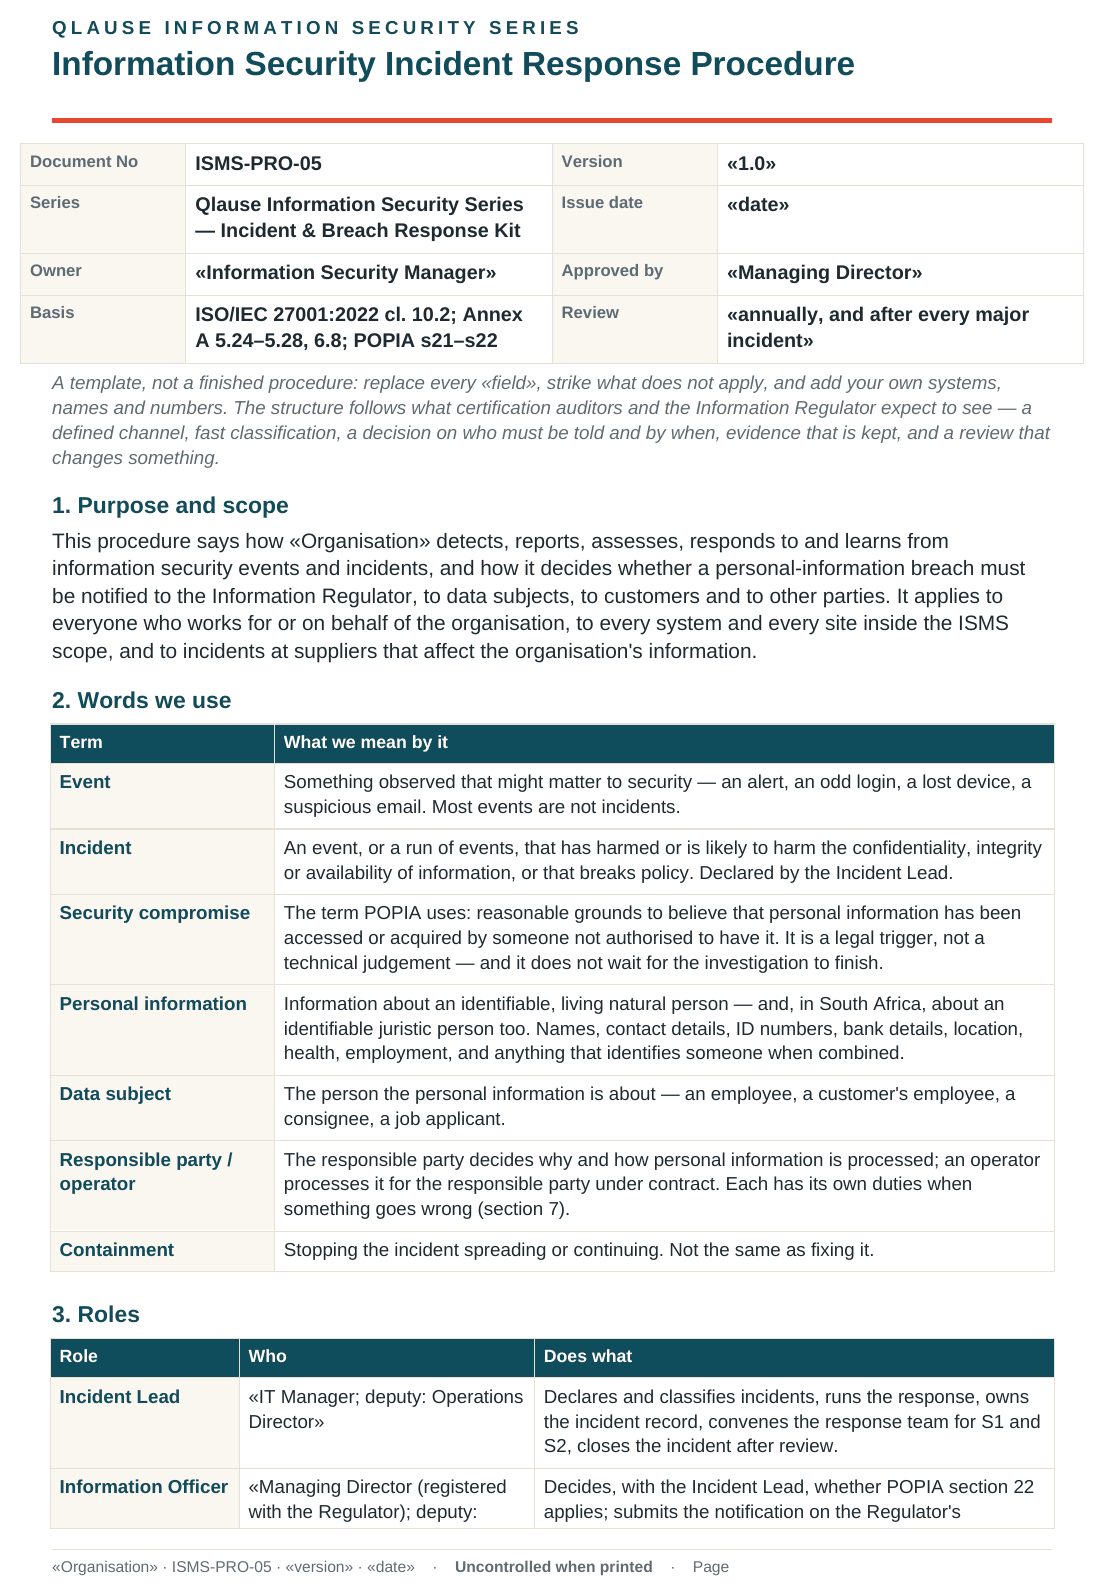
ISMS-PRO-05 Incident Response Procedure (template)
Five pages, Word and PDF: roles, reporting, triage, response, who must be told and by when, evidence, review, records, testing, contact card.
Evidence log, post-incident review, tabletop record
Chain of custody; timeline → five whys → root cause → actions feeding clause 10.2; exercise record with a scored observer checklist.
Two tabletop exercise scripts
Ransomware and business email compromise, 90 minutes each, with injects, expected actions, discussion questions and a debrief record. Word and PDF.
Guidance and worked example
Events, incidents and compromises; the clocks; the three mistakes; what the auditor asks; nine fictional incidents with the full review of one.
One Excel workbook (eleven sheets) and three Word documents with PDF copies, in one zip.
Nine incidents, each with the POPIA answer and the clock
A phishing wave stopped by MFA, a lost driver's phone, misdirected payslips, a supplier's test server holding production data, a cloud account still open as at the reporting date — the register shows which were notifiable, which were not, and why.
See it used

What you still have to do
The kit is the structure and the questions; the judgement is yours. You name the people, set your internal notification target (POPIA says 'as soon as reasonably possible' and gives no hours), adapt the severity grid and, on the day, make the reasonable-grounds call with your Information Officer and write the notice in your own voice from the template. Nothing in it is legal advice: have the procedure and the notice wording checked by a qualified adviser, and check the Information Regulator's current guidance — the regulatory facts are as at October 2026. Written in our own words; no standard or statute text is reproduced.
Who it's for
Information Officers, ISMS leads, IT managers and quality or compliance managers in South African organisations running or building an ISO/IEC 27001 system — and anyone who has just been told 'you are the Information Officer now'.
The details
- Works with
- Word and Excel 2016 or later, including Microsoft 365. Standard .docx and .xlsx files — no macros, no add-ins.
- Licence
- Licensed for your own and your organisation's use — every site and every user, with no per-user fees. Not for resale, redistribution or republication.
- Updates
- Free updates for 12 months after purchase — including when the regulatory position changes — sent as a Payhip product update.
- Refund
- If it isn't right for you, email hello@qlause.app within 14 days of purchase for a full refund. No reason needed.
Questions
Is this legal advice on POPIA?+
No. The kit explains the section 22 duty in plain language, prepares the notification and keeps the clocks; it reproduces no statute text and it is not a substitute for a qualified adviser. Have the procedure and the notice wording checked for your organisation, and check the Information Regulator's current guidance — the facts in the kit are as at October 2026.
Does it set a 72-hour deadline for POPIA?+
No — POPIA says 'as soon as reasonably possible' and gives no hours. The register lets you set your own internal target (72 hours is a defensible default) and treats it as a promise; the 72-hour clock that is law is the GDPR's, and the kit runs that one only where EU or UK people are involved.
We are not ISO 27001 certified. Is it still useful?+
Yes. Every South African responsible party has the POPIA duty whether or not it has an ISMS, and the register, the decision sheet, the Regulator pack and the notices work on their own. The clause references are there for those who are building the system.
Does it include the text of the standard?+
No. Everything is written in our own words and points to clause numbers. You still need your own licensed copy of the standard to work against — from SABS or the ISO store.
Can the whole team use it?+
Yes. One purchase covers your organisation — every site and every user. What it doesn't cover is reselling it, handing it to other organisations or republishing it.
What if it isn't what I need?+
If it isn't right for you, email hello@qlause.app within 14 days of purchase for a full refund. No reason needed.
Information Security Incident & Breach Response Kit (Excel + Word) — the register, the POPIA s22 decision, the Regulator pack, the notices and two tabletop exercises
Instant download · licensed for your whole organisation · 14-day full refund
Start free
Qlause toolkits are interpretive tools written in our own words — not a substitute for the standards, which you need to hold licensed copies of (from SABS or ISO). All templates & toolkits